Organizational scope
Work with supported tenant, child-tenant, and business-unit context. Confirm which records and workflows belong in each team’s view.
 Request a demo
Environment intelligence
Bring assets, identities, software, and controls into a shared context. Investigate the evidence behind a finding and carry it into the decisions your security and IT teams make.
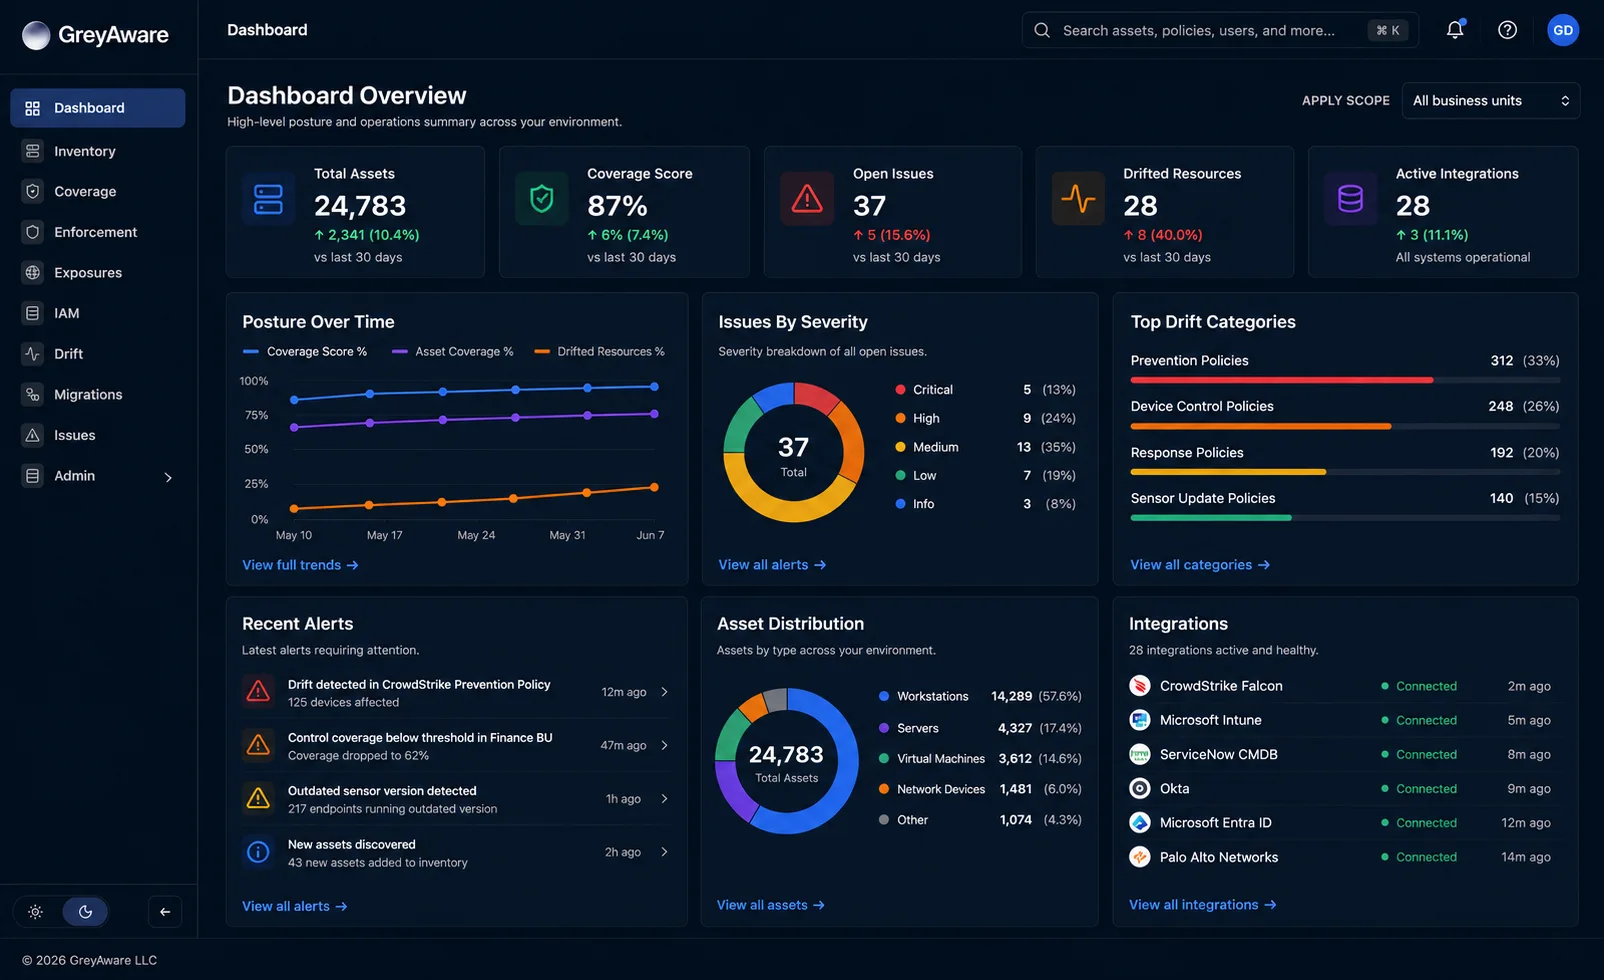
One shared foundation
Your tools describe the environment from different perspectives. GreyAware normalizes supported records, correlates related entities, and retains source context so teams can investigate both the connections and the gaps.
Source records
Connect related records. Preserve their sources. Keep uncertain matches visible.
Decision context
Confirm the integrations, permissions, and data available for your use case. Collection cadence and source quality shape the resulting view.
Review connected entities and their source observations. A match, missing record, or changed value is a starting point for investigation.
Use the available evidence to validate a finding, review a policy, or prepare a migration. Confirm the scope and workflow before taking action.
Connected workflows
Move between inventory, security posture, and change planning with the underlying records in view. Each workflow adds context to the others.
Build context around devices, people, and software.
Compare expectations with the evidence your tools provide.
Keep readiness and validation connected to the plan.
Platform and access
Organizations need to scope work and control access as well as connect data. Bring your team structure and evaluation requirements into the conversation.
Work with supported tenant, child-tenant, and business-unit context. Confirm which records and workflows belong in each team’s view.
Use role-based permissions and membership scope to define access to platform areas and supported actions. Review the required configuration for your environment.
Inspect source observations, evaluation reasons, and available activity history. Check freshness and incomplete information before relying on a result.
Confirm the entities, fields, permissions, and collection cadence supported by each integration. Product names alone do not establish coverage for a specific workflow.
View selected integrationsPlan your evaluation
Bring a question, the tools involved, and the evidence your team needs. We can use that context to define a useful walkthrough.
Choose a recurring question such as a coverage gap, an inventory disagreement, an access review, or a planned control migration. Share the relevant product names and desired outcome; credentials and production exports are not needed in the contact form.
The workflows described here connect data from supported IT and security sources. Collection, control enforcement, deployment, and specialized testing still depend on the tools and operational processes involved. Confirm the division of responsibilities for your use case.
Review the supporting source records, observation timing, matching context, and missing information. An observed assignment, missing control record, or permissive network rule has a specific meaning; the investigation should establish what conclusion that evidence supports.
Capabilities and execution modes vary by workflow and integration. Some workflows provide visibility or preparation only. For example, the current migration implementation supports simulation and dry-run previews, with live submission disabled. Confirm the supported action path during evaluation.
Bring your requirements for team access, source permissions, data handling, and operational review. We can discuss the applicable configuration and documentation. Our published privacy policy and terms are available for an initial review.
Start a conversation
Choose the tools and the workflow that matter most. We’ll walk through how the records connect, what the evidence supports, and where further validation is needed.
Allow Google Analytics to use cookies to help us understand visits and improve the site. Your choice won’t affect contact requests. Privacy details